AIdentity / Counterpoise
Demo environment

Make intelligent operations accountable.

Counterpoise gives organisations practical governance, privacy, ethics, security and assurance controls that fit the way work is actually done.

Counterpoiseorchestrated controls
GGovernance
PPrivacy
EEthics
SSecurity
Verity

Choose the control surface you need

Five capabilities · one expandable platform
✓
Verity sits across the platform.Evidence that controls operated and decisions can be trusted.
Datafolio mark

Datafolio

Keep selected credentials and proof receipts under customer control, then present only what a specific audience needs.

Independent modules

Start with one problem, add capability as your operating maturity grows. Each module has a clear purpose, owner and outcome.

5independent
capabilities

Your evidence, in your hands

Datafolio is the wallet capability for keeping selected credentials, assurance records and proof receipts under customer control. It supports scoped presentation and visible status; it does not decide whether a Counterpoise action is allowed.

01customer
controlled
DATAFOLIO Local demo
YOUR PROOF WALLET

Selected records

Illustrative records only · nothing is transmitted

✓
AI workflow assuranceVerity attestation · scope: onboarding
CURRENT
◈
Decision receiptCounterpoise decision · approved with conditions
VALID
⌁
Data provenance recordSource, version and integrity references
CURRENT

Choose a local demo action to see how scoped sharing and status changes are presented.

Keep selected records

Datafolio can hold or reference customer-selected credentials, manifests and proof receipts. Source business data stays in its approved system by default.

Share to a defined purpose

A presentation can be limited by credential, claim, audience, purpose and validity period, so a reviewer receives only the evidence needed for that interaction.

See status and changes

Expiry, revocation and changed assurance states remain visible. A cryptographic commitment can show whether a presented value matches a recorded state; it does not prove the original source claim was true.

Product boundaryCounterpoise decides and enforces action authority. Verity records assurance evidence. Datafolio gives customers a controlled way to retain and present selected records.
i
Local demonstration only.

The wallet view is illustrative; it does not issue credentials, store customer records, connect to a blockchain or send presentations.

Buyer scenarios

See how different leaders can use the same modular foundation to solve a different business problem.

Deployment choices

Counterpoise can be introduced in the way that fits your risk profile, data environment and pace of adoption.

02

Dedicated environment

A separated operating space for stronger control over configuration and access.

  • Dedicated tenancy
  • Organisation-specific policies
  • Expanded integration options
03

Private or on-premises

For regulated or sensitive environments requiring local control and deployment autonomy.

  • Local data boundary
  • Enterprise security model
  • Deployment-led assurance
i
This demonstration is fully local.

No cloud service, account, API or customer data is connected.

Cloud deployment

A platform-neutral deployment model lets Counterpoise use the customer’s preferred cloud boundary while keeping the control plane, module contracts and assurance model consistent.

Reference deployment patternIllustrative · not a live connection
Customer boundary
Users & systemsIdentity · data · workflows
→
API & identityGateway · SSO · policy context
Counterpoise control planeOrchestrator · approvals · observability
→
Independent enginesGovernance · Privacy · Ethics · Security
Verity assuranceEvidence · lineage · attestations
→
Protected storesEvidence vault · metadata · audit trail
Azure profileAWS profileGCP profileHeroku profilePrivate / on-premises
i
Reference only.

The standalone demo contains no cloud credentials, APIs, telemetry or connected customer data.

System architecture

Explore the complete control path, the modular service boundaries, the decision sequence and the data movement model. These are reference diagrams for the proposed design; this local demo has no live integrations.
4technical
views
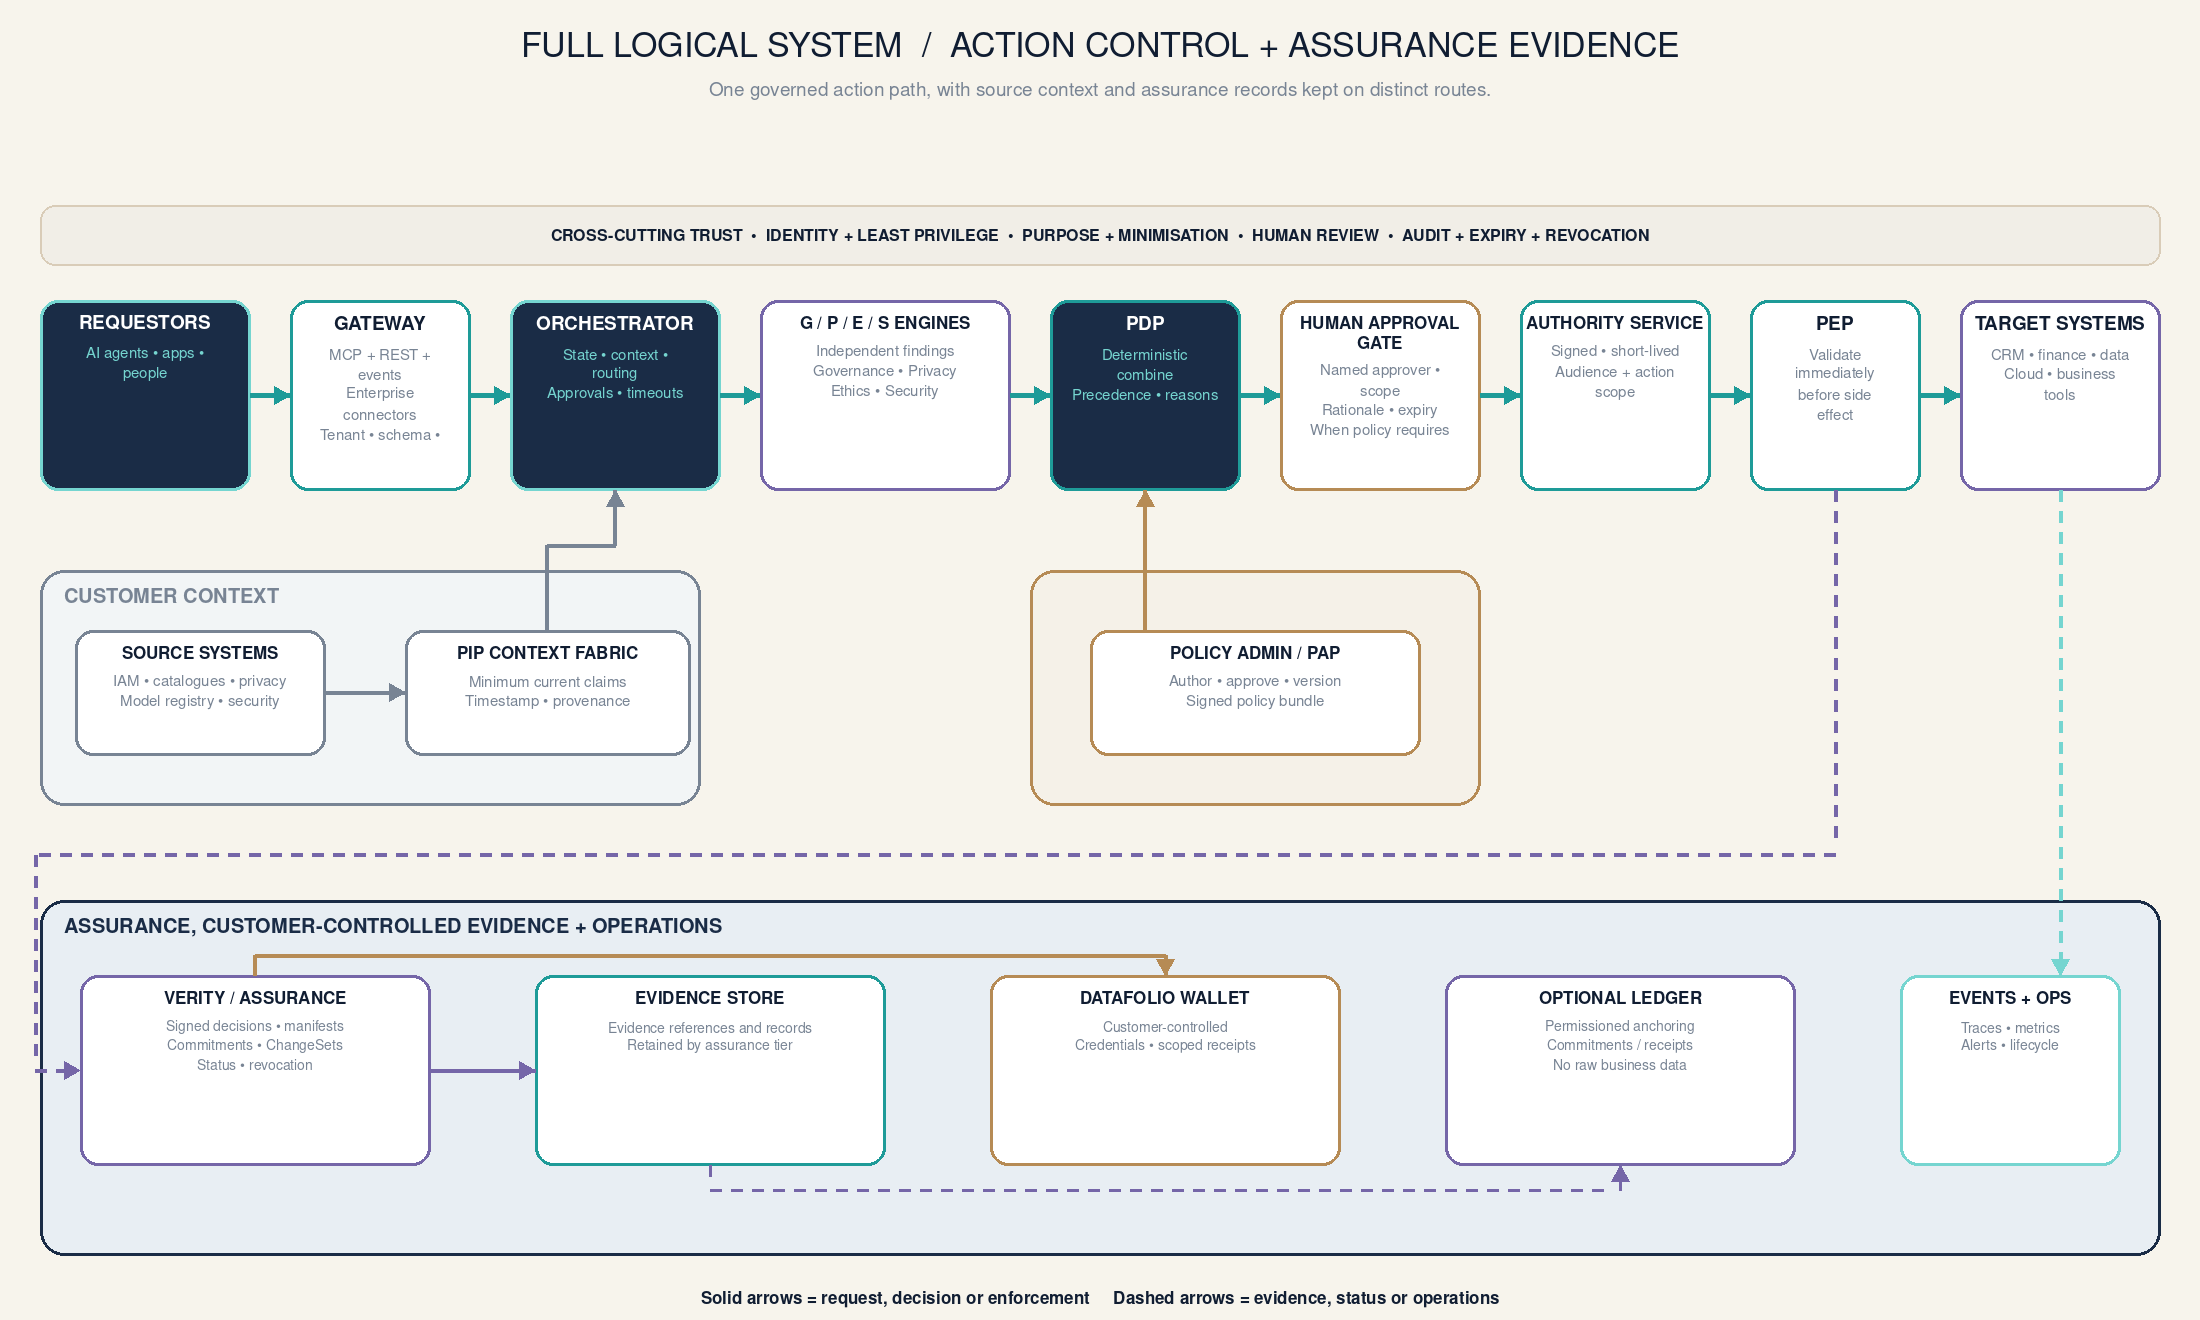
Full logical system architecture showing requestors, gateway, orchestrator, independent Governance, Privacy, Ethics and Security engines, deterministic PDP, human approval, authority service, PEP, target systems, Verity assurance, evidence store, Datafolio wallet and operations.
Full system view · request and enforcement paths are distinct from evidence, status and operations paths.
Open full-size diagram ↗
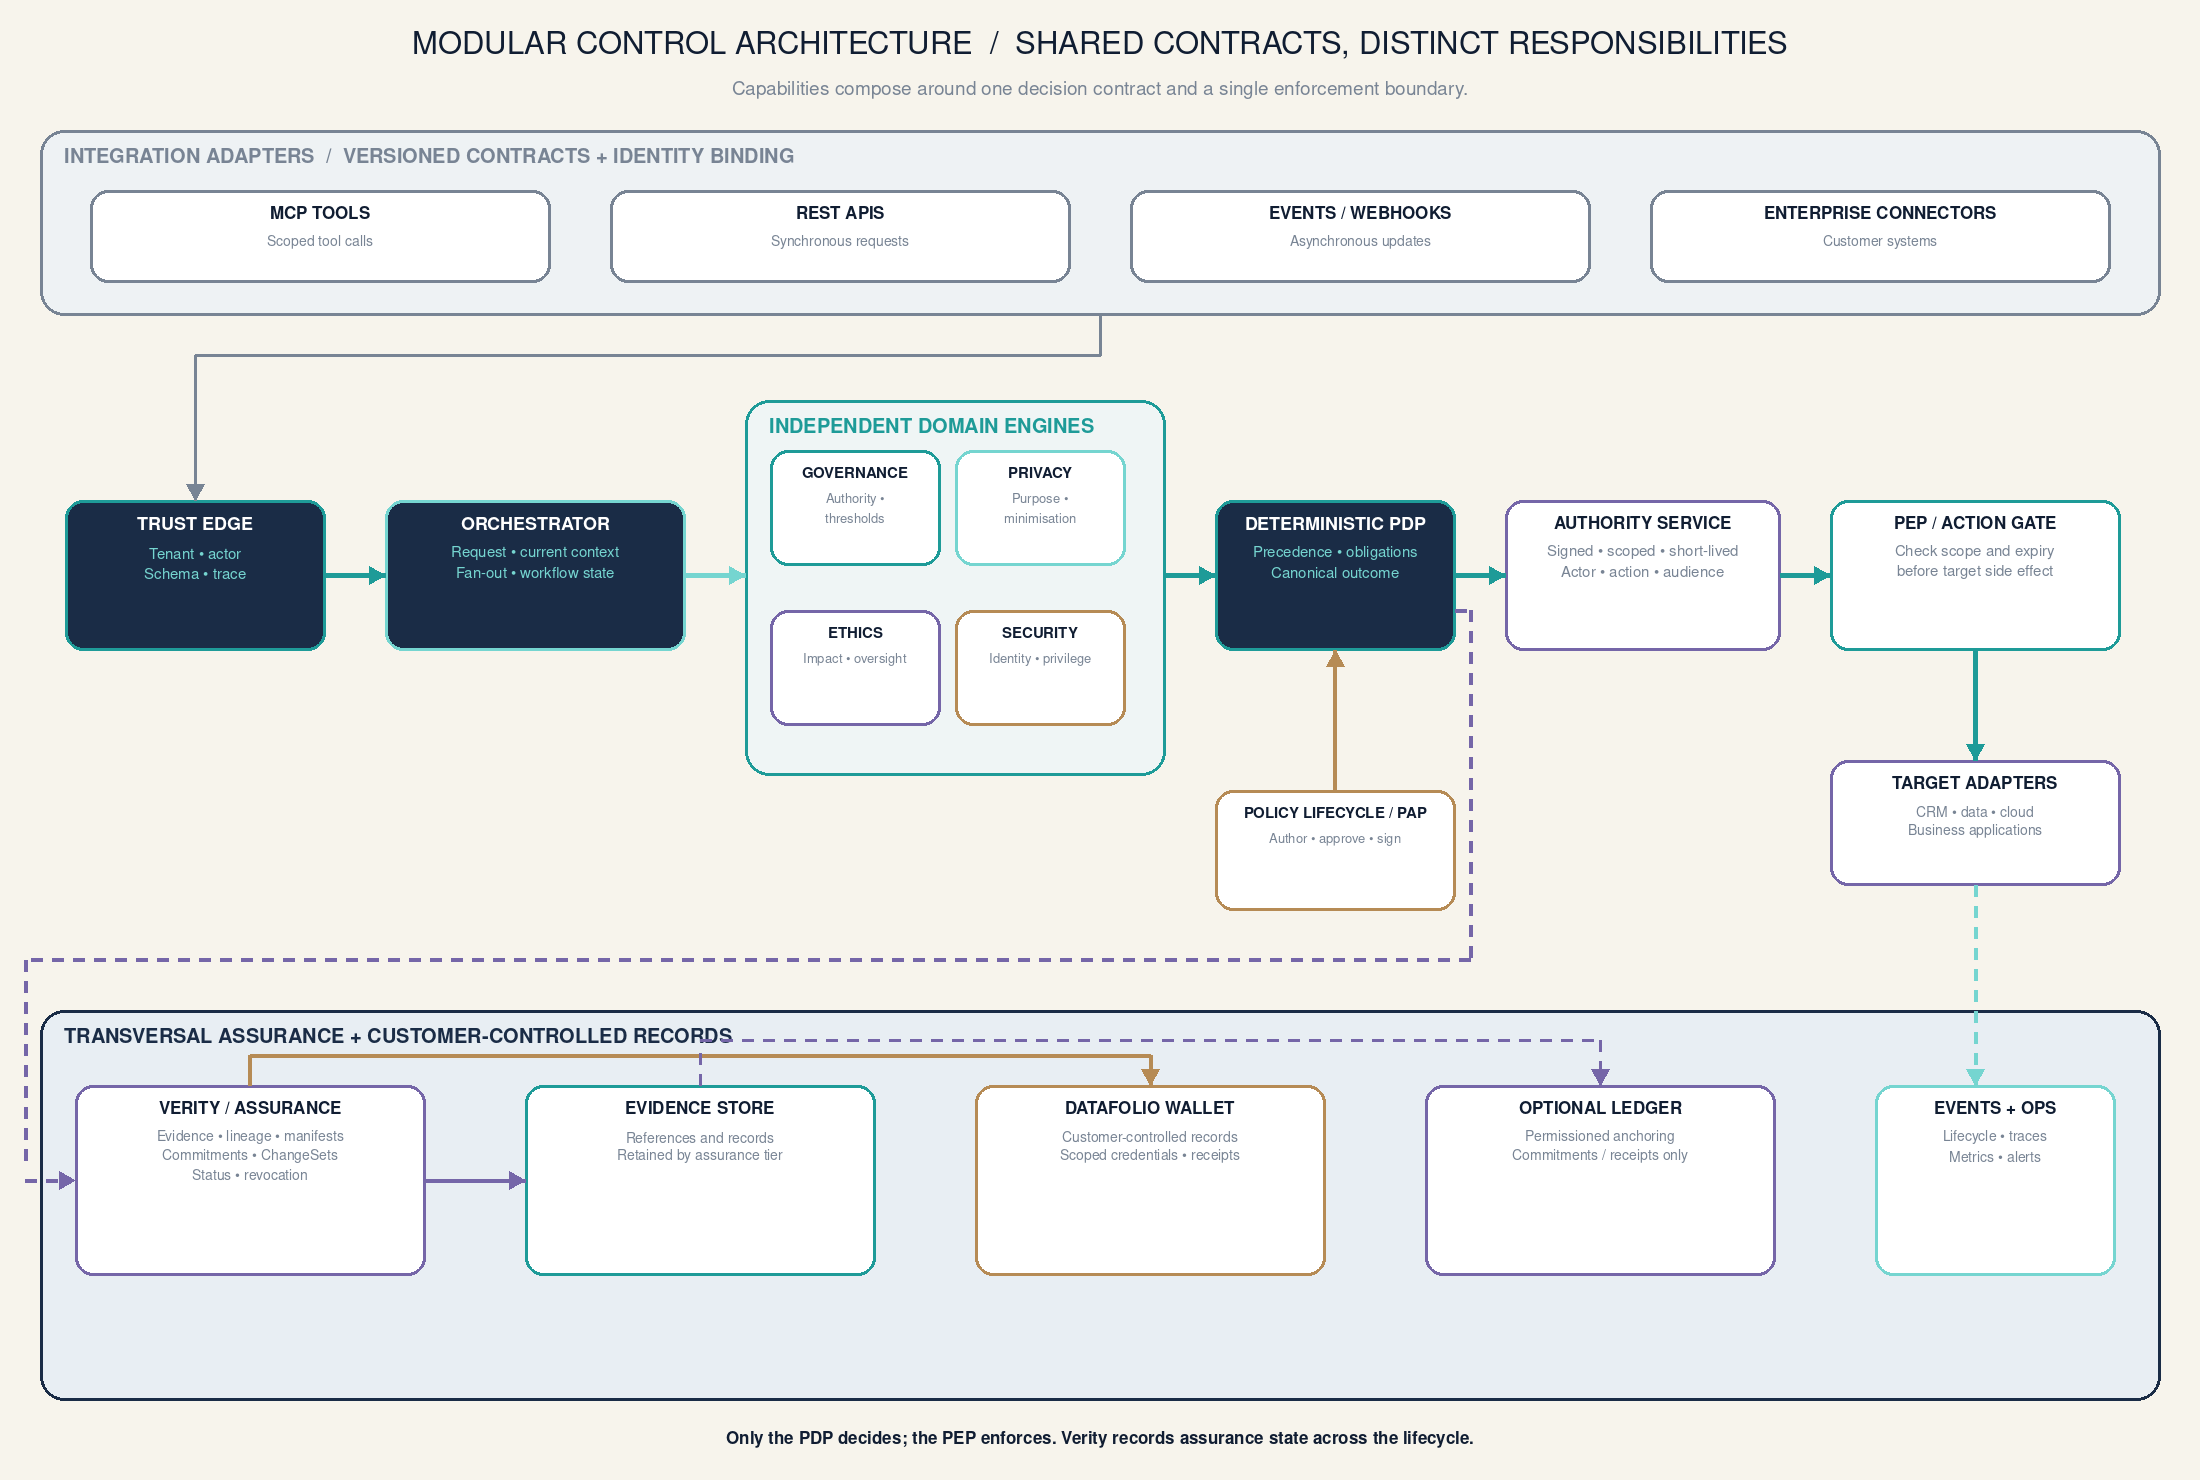
Modular architecture showing integration adapters, shared control plane, independent domain engines, policy administration, deterministic decision, authority and enforcement services, and transversal assurance services.
Modular composition · independent domain engines share contracts and a single controlled enforcement boundary.
Open full-size diagram ↗
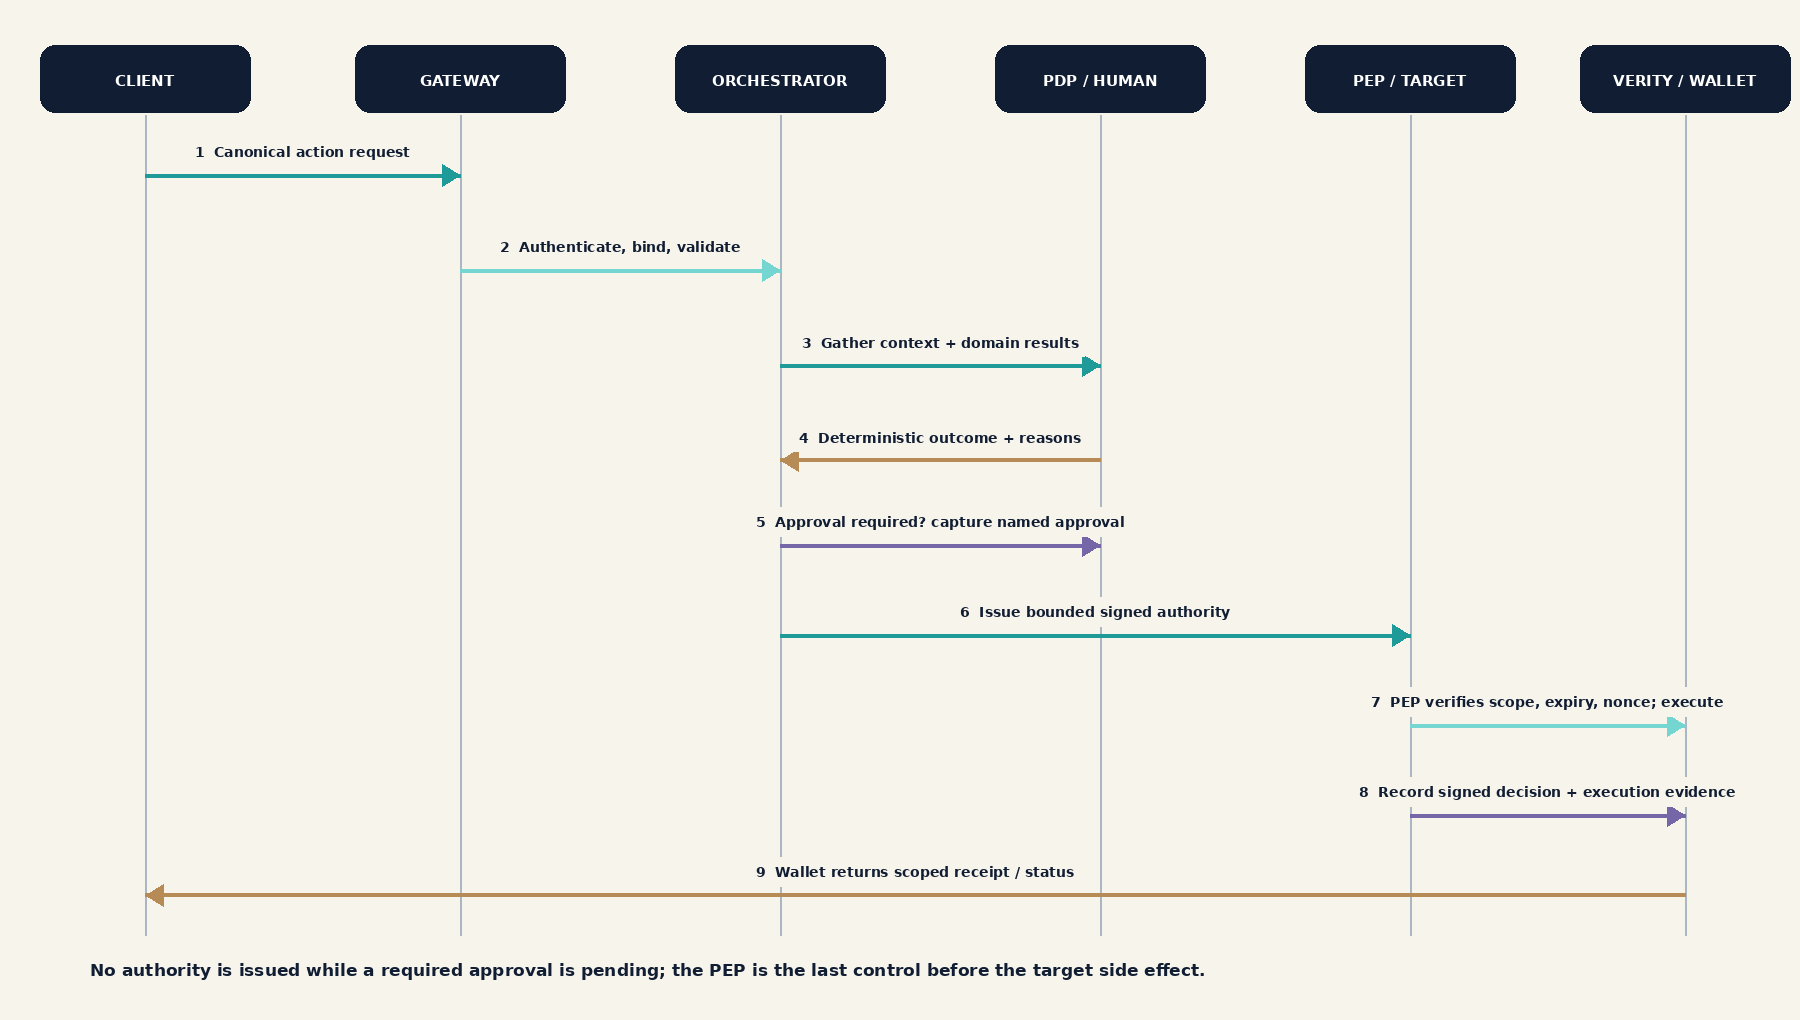
Decision sequence from request receipt and validation through context gathering, domain assessment, policy decision, approval, bounded authority, enforcement and evidence recording.
Decision sequence · no execution authority is issued while a required approval is pending.
Open full-size diagram ↗
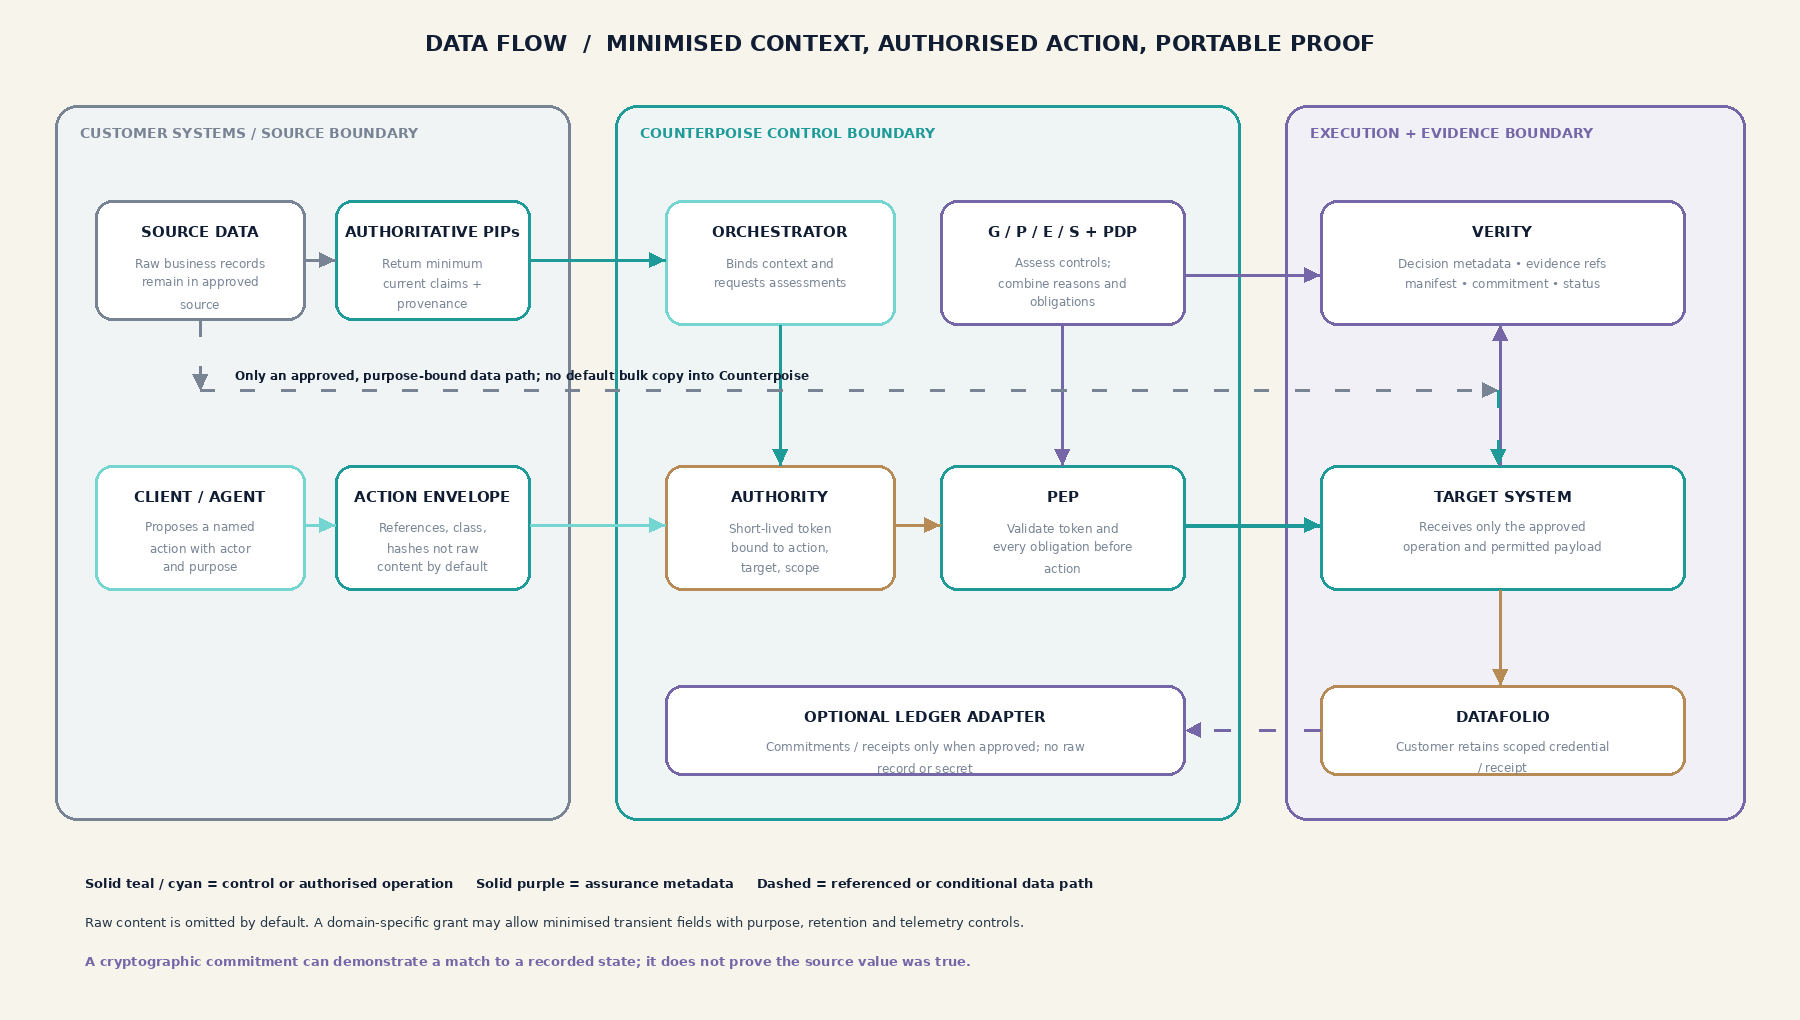
Data-flow diagram separating customer source systems, Counterpoise control plane, authorised execution, Verity evidence and Datafolio wallet receipt.
Data flow · raw source records remain in approved systems by default; the control plane uses minimum necessary context.
Open full-size diagram ↗

Four independent engines

Governance, Privacy, Ethics and Security return separate, explainable findings. Each assesses within its domain and cannot grant execution authority.

One decision, one gate

The deterministic PDP combines required findings under versioned policy. If permitted, the authority service issues scoped, short-lived authority; the PEP validates it immediately before the target action.

Evidence across the lifecycle

Verity records decision context, provenance, attestations and change state. Datafolio can retain customer-selected credentials or receipts; an external ledger remains optional.

System architecture

Explore the complete control path, the modular service boundaries, the decision sequence and the data movement model. These are reference diagrams for the proposed design; this local demo has no live integrations.
4technical
views
Full logical system architecture showing requestors, gateway, orchestrator, independent Governance, Privacy, Ethics and Security engines, deterministic PDP, human approval, authority service, PEP, target systems, Verity assurance, evidence store, Datafolio wallet and operations.
Full system view · request and enforcement paths are distinct from evidence, status and operations paths.
Open full-size diagram ↗
Modular architecture showing integration adapters, shared control plane, independent domain engines, policy administration, deterministic decision, authority and enforcement services, and transversal assurance services.
Modular composition · independent domain engines share contracts and a single controlled enforcement boundary.
Open full-size diagram ↗
Decision sequence from request receipt and validation through context gathering, domain assessment, policy decision, approval, bounded authority, enforcement and evidence recording.
Decision sequence · no execution authority is issued while a required approval is pending.
Open full-size diagram ↗
Data-flow diagram separating customer source systems, Counterpoise control plane, authorised execution, Verity evidence and Datafolio wallet receipt.
Data flow · raw source records remain in approved systems by default; the control plane uses minimum necessary context.
Open full-size diagram ↗

Four independent engines

Governance, Privacy, Ethics and Security return separate, explainable findings. Each assesses within its domain and cannot grant execution authority.

One decision, one gate

The deterministic PDP combines required findings under versioned policy. If permitted, the authority service issues scoped, short-lived authority; the PEP validates it immediately before the target action.

Evidence across the lifecycle

Verity records decision context, provenance, attestations and change state. Datafolio can retain customer-selected credentials or receipts; an external ledger remains optional.

Software architecture

Counterpoise is structured as independent capabilities around a common control plane, with Verity providing the evidence and assurance thread across the workflow.

Experience & integration
Customer workflows, admin console, reporting and external systemsBusiness processes · APIs · events · operator actions
↓ requests, context and decisions ↓
Control plane
OrchestratorRoutes requests, applies policy context and coordinates outcomes
Decision & approval servicesPDP / PEP · human approval · escalation · revocation
ObservabilityHealth · events · change · operational evidence
↓ governed evaluation ↓
Independent capability modules
GovernanceOwnership & decisions
PrivacyPurpose & data use
EthicsImpact & oversight
SecurityAccess & resilience
↓ evidence and assurance ↓
Counterpoise Verity
Evidence, provenance, lineage, attestations and assurance recordsCreates a durable, reviewable account of what was evaluated, decided and changed

Stable interfaces

Modules communicate through versioned API, event and policy contracts so capability can evolve without redesigning the whole platform.

Controlled execution

Identity, least privilege, approval gates, signed authority and continuous revocation sit around the execution path.

Observable by design

Events, health, change and evidence signals support operational oversight across multi-tenant, dedicated and private profiles.

Verity dashboard

See which decision-critical assets are assured, what changed, and where a customer action is needed. This illustrative view is designed for operational owners, risk leaders and reviewers.

Assurance postureIllustrative customer view · refreshed just now
✓
82%assured coverage
+6% this month
!
3changed pending review
2 due today
↗
1drifted asset
action required
⌁
146evidence records
+18 this month

Assurance by state

Last 30 days ▾
82%assured
Assured 32Changed pending 3Drifted 1Other / not yet assessed 3
Coverage across decision-critical assets39 of 47

Priority actions

4 open

Evidence coverage

Asset / decisionOwnerLast evidenceState
i

Verity is the assurance and evidence capability within Counterpoise. Statuses are illustrative and demonstrate how provenance, checks, changes and attestations can be presented to customers.

From source to trusted evidence

Verity turns important data and decisions into a reviewable evidence trail: what entered the workflow, what checks ran, what changed, who acted and what assurance state applies now.

01Sources & eventsSystems · files · APIs · workflow actions
→
02CanonicaliseNormalised commitments and identity context
→
03Generate evidenceChecks · lineage · policy results · attestations
→
04Proof & detect changeAssetManifest · Merkle-root proof · drift signals
Decision 7F2A · v1.4

Canonical commitment → evidence set → proof reference → named attestation

Reviewable and exportable
ASSUREDCHANGED_PENDINGDRIFTEDESCALATEDNON_COMPLIANTREVOKED
Operational dashboardOwners see what needs action now
Credentials & presentationsShare bounded proof with reviewers
Audit and assurance packExplain what happened and why it can be trusted

Where did it come from?

Source identity, time, lineage and handling context remain visible around each assurance record.

What changed?

Canonical commitments and proof references make unexpected change visible for review and escalation.

Who decided?

Named owners, checks, approvals and attestations connect evidence to responsibility.